
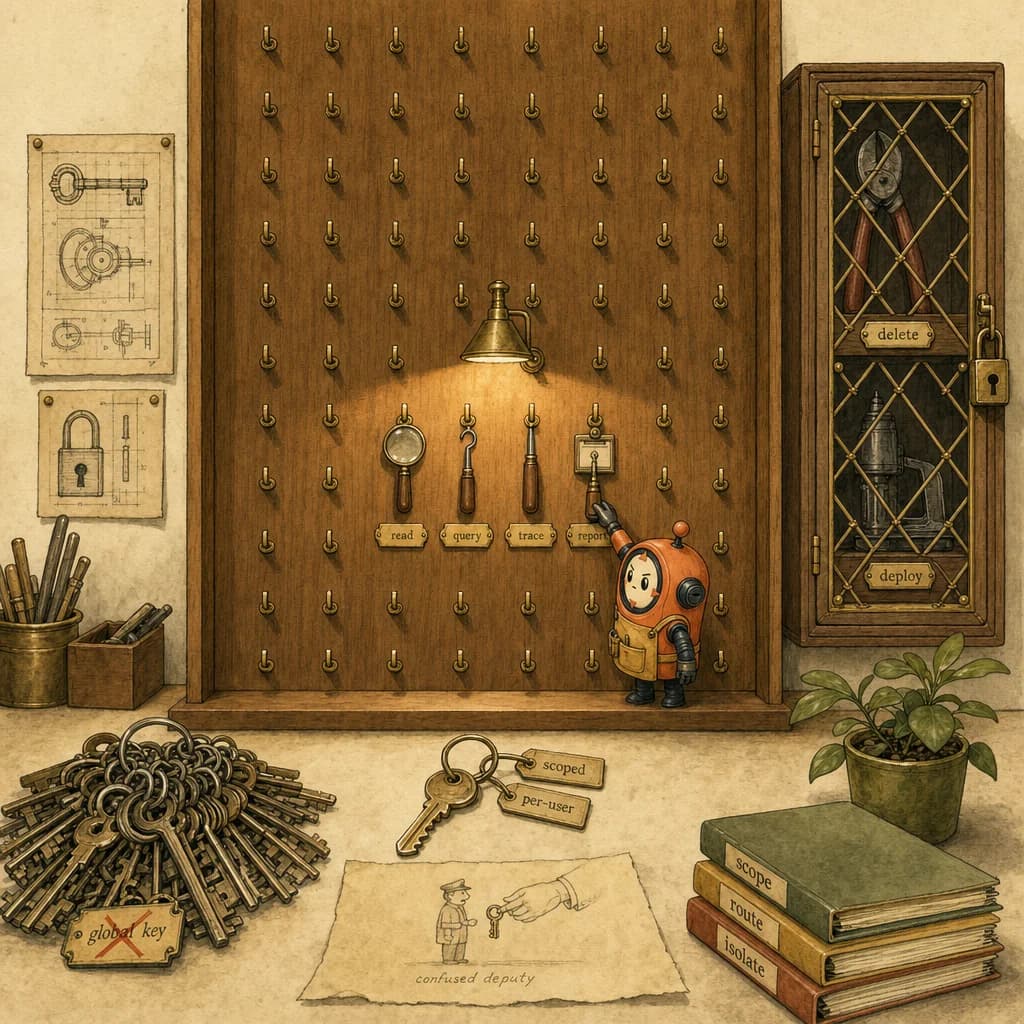
- ✓Give an agent only the tools a task needs, not every tool you have. A large tool set burns context on descriptions before any work happens and widens the blast radius if the agent is prompt-injected. For CCA-F D2, the skill is scoping the tool surface and the token, not maximizing it.
- ✓Minimal Tool Surface is an MCP design decision: which server tools you expose, scoped how. Start at the MCP primitive.
- ✓Every exposed tool is a description the model must read and reason over. Tool-calling mechanics explain why more tools means more cost and more confusion.
- ✓When the surface is large, the model's tool-selection accuracy drops. Tool choice is the lever Minimal Tool Surface protects.
Quick answer
Give an agent only the tools the task needs, not every tool you have. A large tool set burns context on tool descriptions before any real work happens, and it widens the blast radius if the agent is prompt-injected. The CCA-F D2 skill is scoping the tool surface, not maximizing it: fewer tools, least-privilege credentials, task-relevant routing.
What is the Minimal Tool Surface
When a vendor ships an MCP server, the tempting move is to wire every tool it offers into your agent. Weights and Biases shipping an MCP server for experiment data is a recent example (first-hand: MCP servers commonly expose a broad tool set), and the instinct is the same every time: more tools, more autonomy.
The instinct is wrong past a small number of tools. Two costs grow with every tool you expose:
- Context cost. Each tool puts its name, description, and parameter schema into the model's context on every call. The agent pays to read all of them before it does anything useful.
- Security cost. Every tool the agent can call is something a prompt-injected agent can also call. Broad access is broad blast radius.
The better pattern: expose only the tools the current task needs, scoped with least-privilege credentials. Call it the Minimal Tool Surface.
More tools vs. minimal surface
| Dimension | Expose every tool | Minimal Tool Surface |
|---|---|---|
| Context window | Filled with tool descriptions before work starts | Spent on the task, not the menu |
| Tool-selection accuracy | Drops as the model picks among many lookalikes | Higher: fewer, clearly relevant tools |
| Credentials | One broad/global key | Per-user, least-privilege tokens |
| Blast radius if injected | Everything the key can reach | Only the scoped task |
| Cost per call | Pays to read unused descriptions | Pays for what it uses |
| Right setting | A throwaway demo | Anything real |
How scoping actually works
Minimal Tool Surface has two independent dials, and you turn both.
- Surface (which tools the model sees). Route only task-relevant tools into context. A research step does not need the deployment tools; a read step does not need the delete tools. Some teams build a tool-router that selects the relevant subset per task instead of loading the full catalog.
- Privilege (what each tool can do). Back each tool with a scoped, per-user token, never a global service-account key. Then even a tool the agent legitimately holds cannot act outside its lane.
Worked example - "let an agent inspect ML runs, safely."
- Scope the surface: expose only the read/query tools for this task, not the registry-promote or delete tools.
- Scope the credential: issue a per-user token limited to that user's projects, not a global key.
- Isolate execution: if the agent runs shell commands, run them in a sandbox, not on the host.
- Verify before trust: treat tool output as input to check, not fact, the same judge discipline you apply to any agent step.
That is a Minimal Tool Surface: small menu, narrow keys, isolated execution.
A name for the trap: the Confused Deputy
The Confused Deputy - an agent holding broad credentials is tricked (often by prompt injection) into using those credentials for something the attacker could not do directly. The fix is not a smarter agent; it is a smaller key. Least-privilege scoping turns a catastrophic blast radius into a contained one.
This is a long-standing security concept, not a new one (first-hand: the Confused Deputy is a classic capability-security problem), and MCP makes it newly relevant because agents now hold real credentials and act on them.
Why it matters for CCA-F
This is the heart of D2 - Tool Design & MCP Integration, which is 18% of the exam and overlaps tool choice and context management.
The proprietary read: D2 questions reward scoping judgment, not tool count.
- Old instinct: give the agent everything so it can handle anything.
- D2 instinct: give the agent the smallest sufficient tool set, scoped with least-privilege credentials, and route by task.
The distractor pattern to memorize. On D2 scenarios where an agent picks the wrong tool, leaks data, or runs up token cost, the trap answers are "expose more tools," "use a bigger model," or "add more examples." The architecturally correct move is one of:
- Narrow the surface (route only task-relevant tools), or
- Scope the credential (per-user, least-privilege), or
- Isolate execution (sandbox shell/tool calls).
See agentic tool design for the canonical D2 scenario, and tool-call skipping for the failure mode a clean surface helps prevent.
How to apply it
- Start from the task, not the catalog. List the tools this task actually needs, then expose only those.
- Default to per-user tokens. Never hand an agent a global key when a scoped one will do.
- Separate read from write. Keep destructive tools out of read-only tasks entirely.
- Isolate shell/tool execution. Run untrusted execution in a sandbox, not on the host.
- Treat tool output as unverified. Check it; do not merge it on faith.
- Measure the surface. If your agent loads dozens of tools per call, that is a design smell, not a capability.
The meta-skill, and the D2 exam skill, is the same: capability comes from the right tools scoped well, not from the most tools.
5 direct routes into the scored material.
- conceptsMinimal Tool Surface is an MCP design decision: which server tools you expose, scoped how. Start at the MCP primitive.
- conceptsEvery exposed tool is a description the model must read and reason over. Tool-calling mechanics explain why more tools means more cost and more confusion.
- conceptsWhen the surface is large, the model's tool-selection accuracy drops. Tool choice is the lever Minimal Tool Surface protects.
- scenariosThe canonical D2 scenario: designing the tool set an agent sees. Minimal Tool Surface is its core principle.
- exam-guideD2 (Tool Design & MCP Integration) is 18% of the exam and rewards scoping decisions over tool count.
Share this post.
One share is one less person stuck on the same question.